
Otoroshi extension · Open source
Threat Protection Suite
A WAF, IP reputation, bot control and a decision fabric for Otoroshi.
A JVM-native ModSecurity WAF with the OWASP Core Rule Set, threat-intel feeds, CrowdSec, bot mitigation and one threat score for every request — with Threat Studio, the security console for Otoroshi.
- Stars
- 0
- Language
- Scala
- License
- Apache-2.0
- Last update
- today
# 1. download the latest release jar
#    https://github.com/cloud-apim/otoroshi-waf-extension/releases/latest
# 2. start Otoroshi with the extension on the classpath
java -cp "./otoroshi-waf-extension.jar:./otoroshi.jar" \
  -Dotoroshi.storage=file \
  play.core.server.ProdServerStart
Features
What's inside
JVM-native WAF
ModSecurity SecLang rules with the OWASP Core Rule Set embedded, upload scanning, signed rule feeds and virtual patches.
IP reputation
Curated threat-intel feeds, CrowdSec in both directions, ASN classification and geolocation.
One threat score
Every detector adds up into a shared score, and the response is graded — log, challenge, throttle, tarpit, deny or ban.
Cluster-wide bans
Bans, distributed fail2ban and correlated incidents shared by every node of the cluster.
Bots & AI crawlers
Proof-of-work challenge, CAPTCHA backends, verified crawlers, AI-crawler policy with generated robots.txt and llms.txt, honeypots.
API security
OpenAPI contract enforcement, behaviour guards (login, traffic, BOLA), error leakage and sensitive-data masking.
Alerting & SIEM
Slack, Teams, PagerDuty, webhooks and OCSF events for your SIEM.
Dry run first
Everything starts in dry run. A learning mode and a false-positive tuning assistant help you arm with confidence.
Threat Studio
The security console for Otoroshi, with route posture, incidents, analytics and fleet views.
Decision fabric
Every threat.
One score.
The fastest correct path is the preset plugin: one slot on a route that expands into the whole detection fabric, in the order that makes it work. Create a threat policy (it starts in dry run), a WAF config importing the Core Rule Set, a threat feed — then read the events for a week and arm the switches one at a time.
POST /login?user=admin'--
from 203.0.113.42 · hosting network
- IP reputation+40
- Hosting network (ASN)+15
- WAF · OWASP CRS+45
- Bots & AI crawlers—
- CrowdSec—
- Honeypots—
100
threat score
Threat Studio
The security console
for Otoroshi.
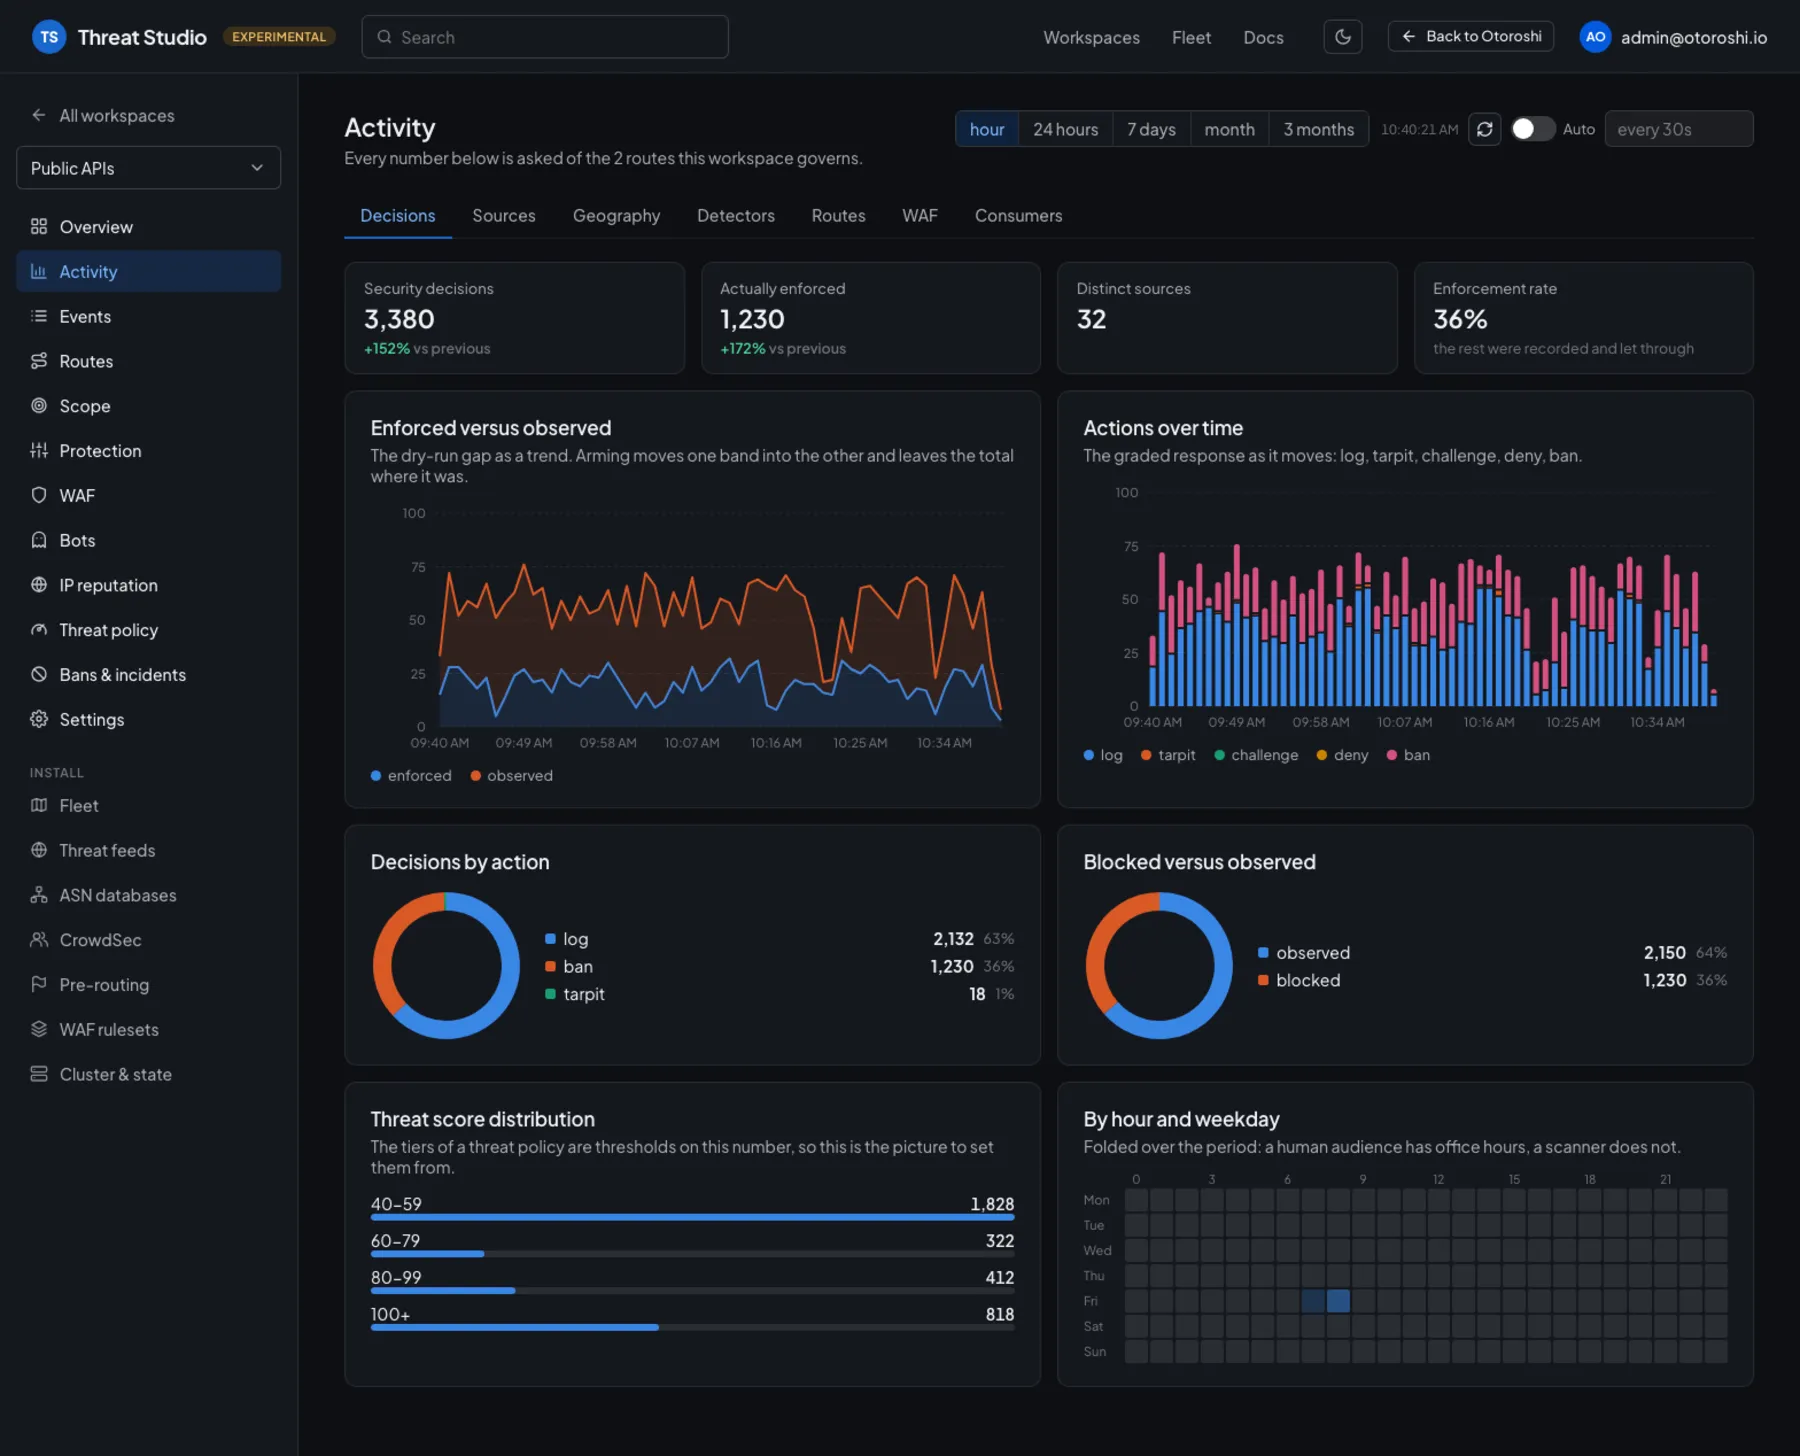
Observe what was blocked, challenged or only recorded, and why. Route posture shows which routes are protected; activity, incidents and dozens of analytics views help you tune policies before enforcing them.
Incidents
From signals
to incidents.
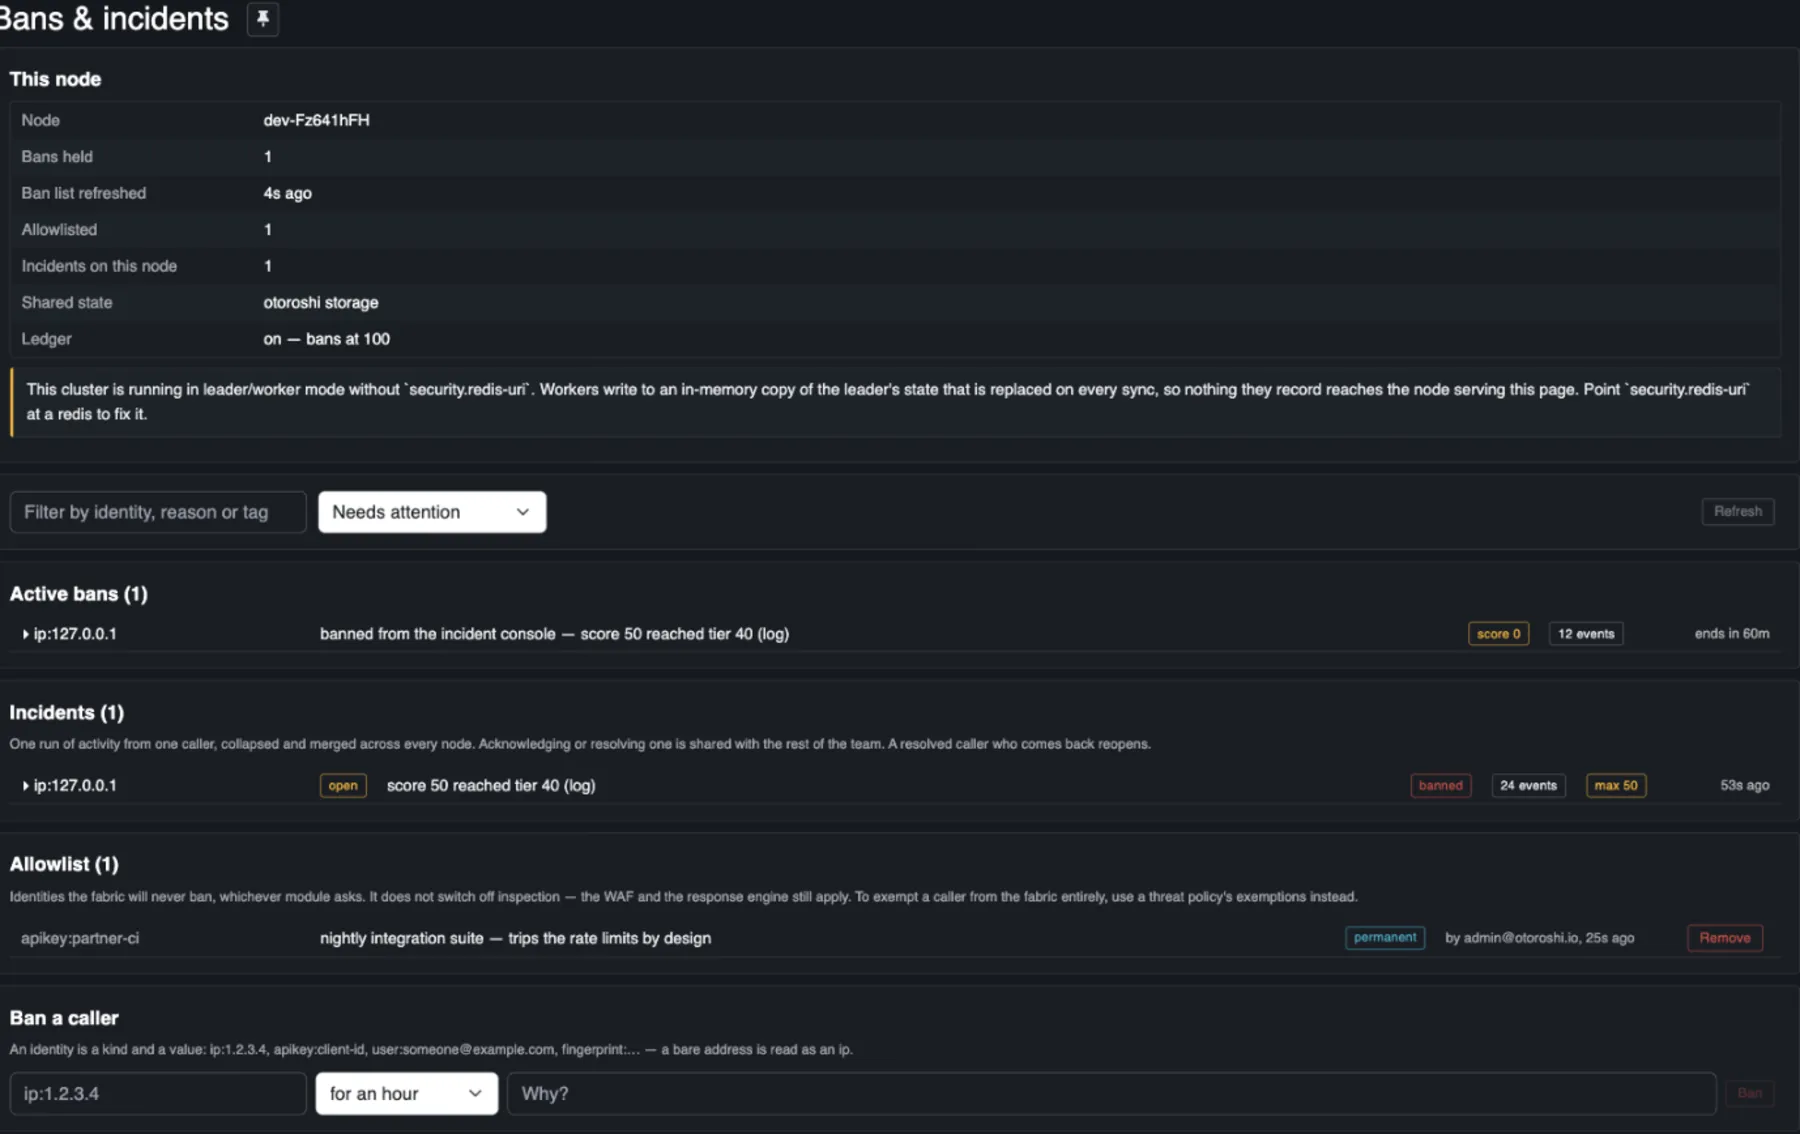
Correlated incidents group related decisions across the cluster, with the evidence behind every ban, and alerting to the tools your team already uses.
Threat Studio Enterprise
Share Threat Studio with every team
Route owners, on-call responders and auditors, each with a role on their own routes, signed in with your company login, with secrets kept on the server and an audit trail.
More open-source projects
Run it in productionwithout running Otoroshi.
Our extensions are available on Otoroshi Managed, fully operated by the people that wrote them. Or get professional support for your own clusters.